Governance, Risk & Compliance

PCI DSS Consulting & QSA Assessment

Support merchants and service providers through PCI DSS scoping, readiness and the appropriate assessment process.

Discuss your requirements
Which systems handle card data during a payment?
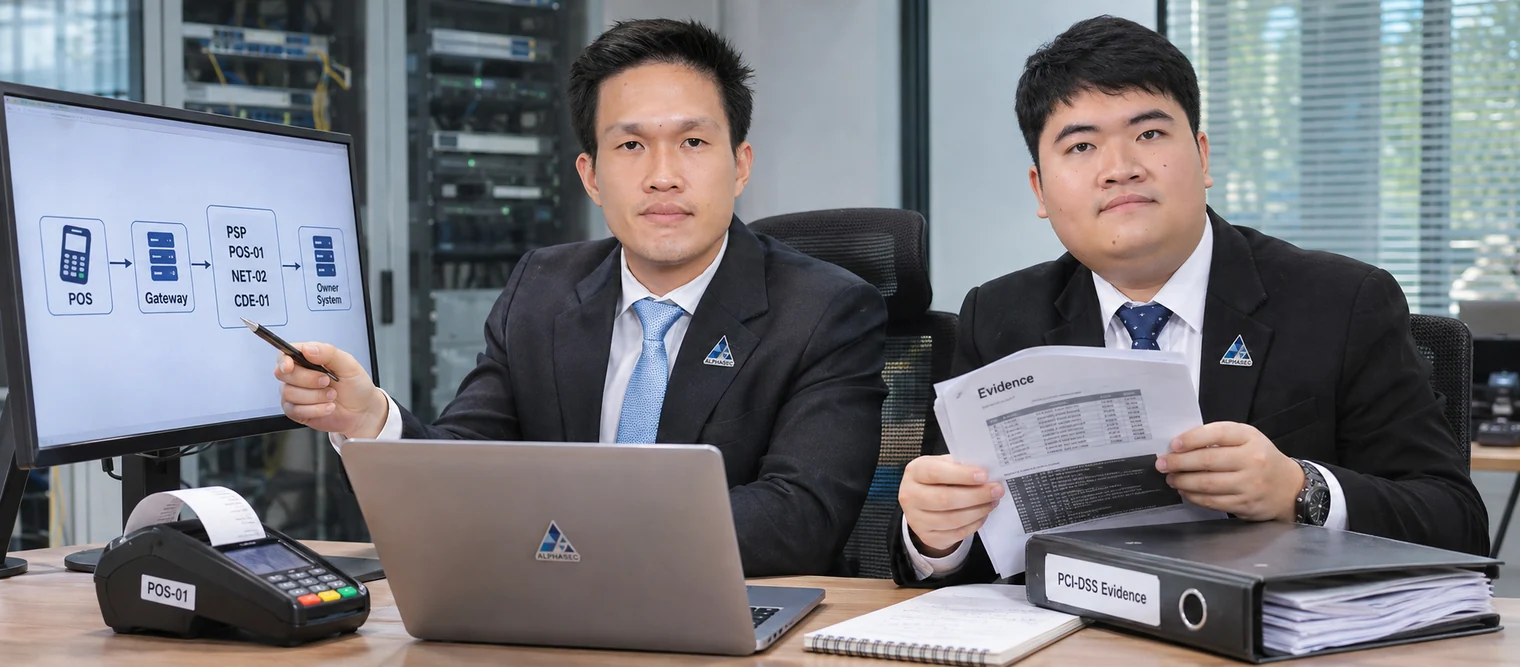
Illustrative scene with the ALPHASEC team · An assessor mapping a merchant payment flow beside a card terminal
Illustrative evidenceData flow
POS card capture → payment gateway → PSP
Illustrative evidenceAssessment boundary
POS-01 / NET-02 / PSP
Illustrative evidenceDelivery plan
CDE-01 → system owner → evidence
A merchant uses several payment channels and an external processor.
  • Scoping / Gap Assessment
  • ROC / AOC
  • SAQ
  • Merchant / Service Provider

SERVICE IN DETAIL

From the first assessment to practical outcomes

Who this service is for

Organisations building a management framework, preparing for customer requirements or improving an existing programme.

How we work

  1. Assessment & gap analysis

    Payment channels, cardholder data flows, third parties and assessment eligibility

    Interview process owners, examine the current documents and sample supporting records. Identify gaps against the agreed framework and distinguish missing controls from controls that lack operating evidence.

  2. Implementation roadmap

    In-scope controls, segmentation, operating records and technical testing evidence

    Prioritise actions by business risk and dependencies. Work with your owners on policies, procedures, responsibilities and practical evidence templates, then support adoption through agreed working sessions.

  3. Assessment & assurance reporting

    Appropriate ROC/AOC reporting or SAQ support, findings and corrective actions

    Present findings with risk, evidence and practical recommendations. Agree management responses, owners and target dates; review corrective evidence where follow-up is included. Any formal assurance conclusion depends on the applicable criteria and assessment results.

What you receive

  • Gap assessment and prioritised action register
  • Agreed policies, working templates and implementation roadmap
  • Assessment report, supporting evidence and corrective-action register appropriate to the agreed assurance route

Relevant frameworks and guidance

Before we begin

We confirm the scope, responsibilities, evidence, timetable and deliverables in the proposal. The activities above are tailored to the systems and objectives agreed with your organisation.

Discuss your scope

Specialist services

Approved Scanning Vendor Scan Coordination

Coordinate external vulnerability scans through an Approved Scanning Vendor, with support for findings review and rescanning.
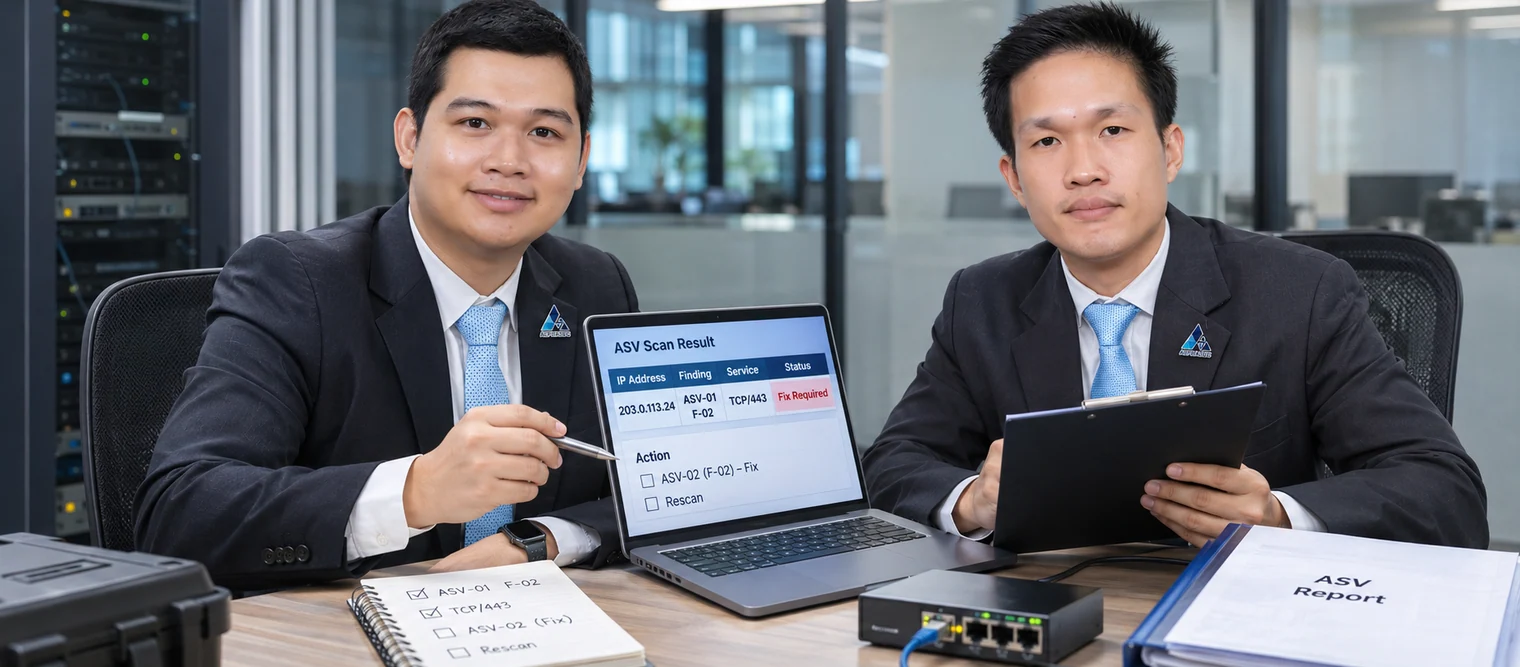
How should an external ASV finding be closed?
Illustrative scene with the ALPHASEC team · An engineer reconciling an external scan finding with the gateway inventory
Illustrative evidenceAssessment boundary
203.0.113.24 · ASV-01
Illustrative evidenceReview finding
F-02 · TCP/443 → network team · remediate
Illustrative evidenceVerification result
ASV-02 · F-02 → retest
The business confirms its external IP scope with the scanning vendor.
View scope, process and deliverables

Who this service is for

IT and development teams preparing a release, validating security improvements or checking business-critical systems.

How we work

  1. Scope & rules of engagement

    External scanning scope and coordination with an Approved Scanning Vendor

    Agree the targets, access levels, test window, business constraints and stop conditions. Confirm written authorisation and prepare the accounts, network access or test data needed for the selected assessment.

  2. Testing & validation

    ASV scan scheduling, findings review, exceptions and remediation coordination

    Combine relevant tools with analyst review for the agreed test objectives. Validate findings, capture reproducible evidence and distinguish confirmed issues from results that need additional information or investigation.

  3. Remediation & retest

    Vendor-issued scan results and agreed rescan follow-up

    Explain business impact, affected components and actionable fixes in a technical report and management summary. Where agreed, retest corrected issues and record their status without treating untested systems as covered.

What you receive

  • Agreed scope and test plan
  • Technical findings with evidence and remediation priorities
  • Executive summary and agreed retest record

External ASV scan results are issued by the selected Approved Scanning Vendor. ALPHASEC coordinates scope, remediation and follow-up.

Relevant frameworks and guidance
Discuss this service

PCI CPSA (Physical & Logical)

Card Production Security Assessment covering physical protection of production and provisioning facilities, and logical security of card data, personalisation, PIN and cryptographic key processes. Scope is defined separately for Physical and Logical requirements.

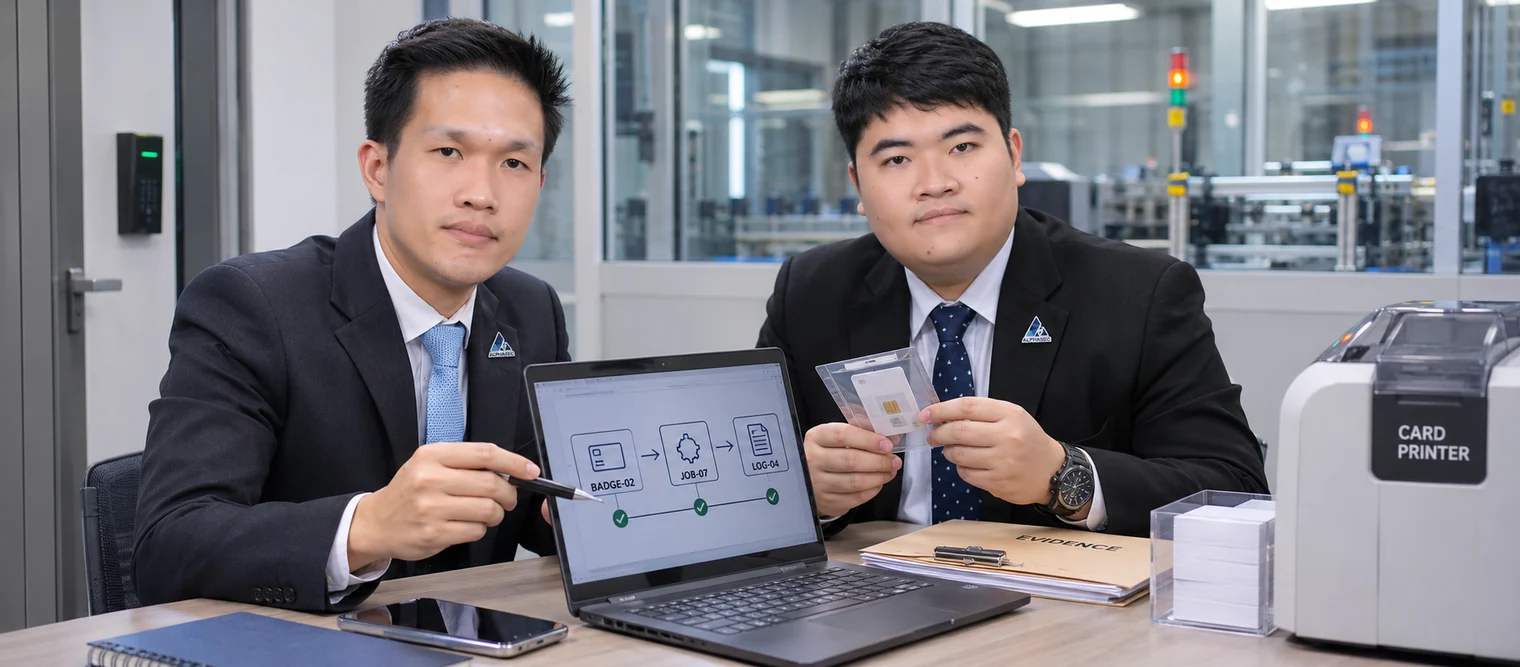
How is card personalisation protected across facility and system boundaries?
Illustrative scene with the ALPHASEC team · An assessor observing a card-personalisation line in a controlled facility
Illustrative evidenceAssessment boundary
ZONE-P / HOST-L · scope
Illustrative evidenceSupporting evidence
BADGE-02 ↔ JOB-07 ↔ LOG-04
Illustrative evidenceReview finding
ZONE-P / HOST-L → evidence · in review
The producer identifies production zones and personalisation systems.
Discuss this service

PCI DSS QSA

Qualified Security Assessor assessment of the cardholder data environment against the Payment Card Industry Data Security Standard. Define scope, review controls and evidence, and prepare assessment reporting such as the Report on Compliance (ROC) and Attestation of Compliance (AOC), as applicable.

Does the evidence support the controls over the review period?
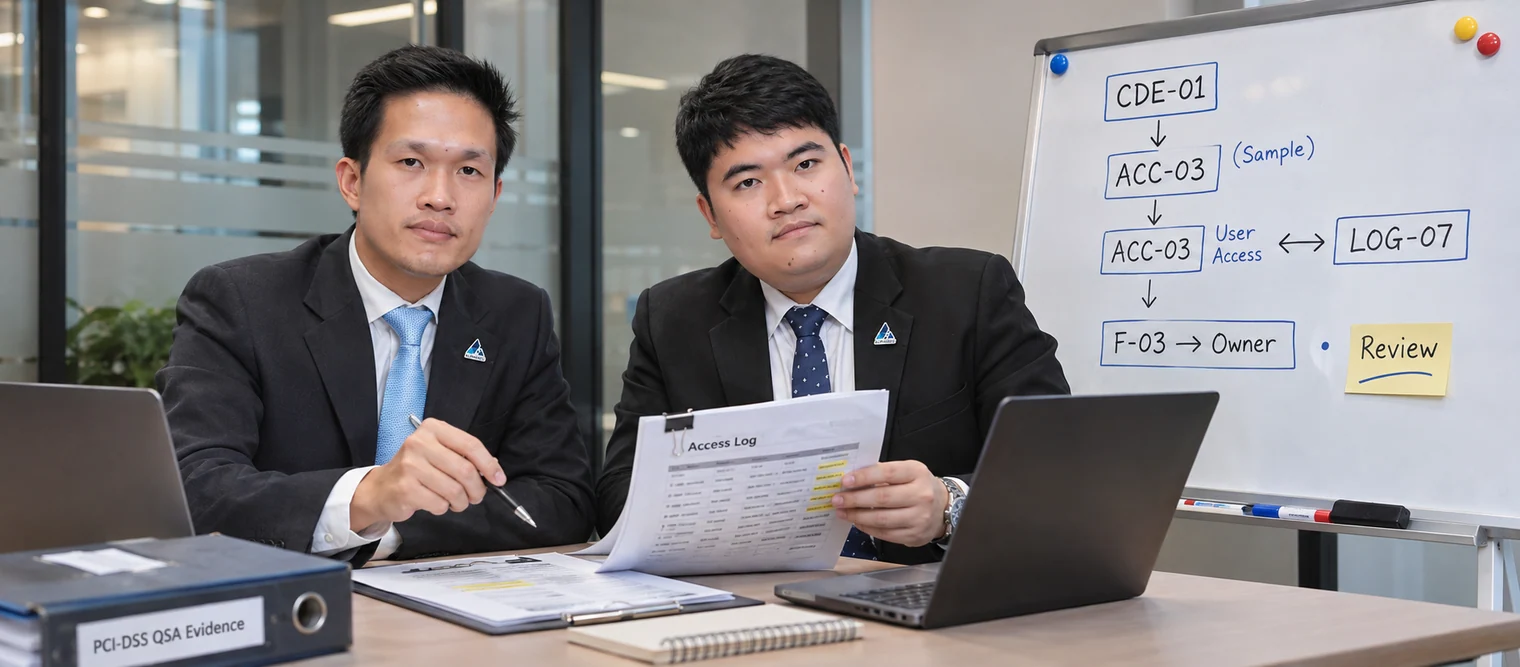
Illustrative scene with the ALPHASEC team · An assessor sampling access evidence with a payment-system owner
Illustrative evidenceAssessment boundary
CDE-01 · sample ACC-03
Illustrative evidenceSupporting evidence
ACC-03 · user access ↔ LOG-07
Illustrative evidenceReview finding
F-03 → system owner · in review
The entity defines its cardholder data environment and assessment period.
Discuss this service

PCI 3DS QSA / 3DS Assessor

PCI 3DS Core assessment for EMV 3-D Secure authentication environments by a 3DS Assessor. Review applicable Access Control Server (ACS), Directory Server (DS) and 3DS Server environments, including access controls, data protection and security monitoring.

Which parts of the authentication service fall in 3DS scope?
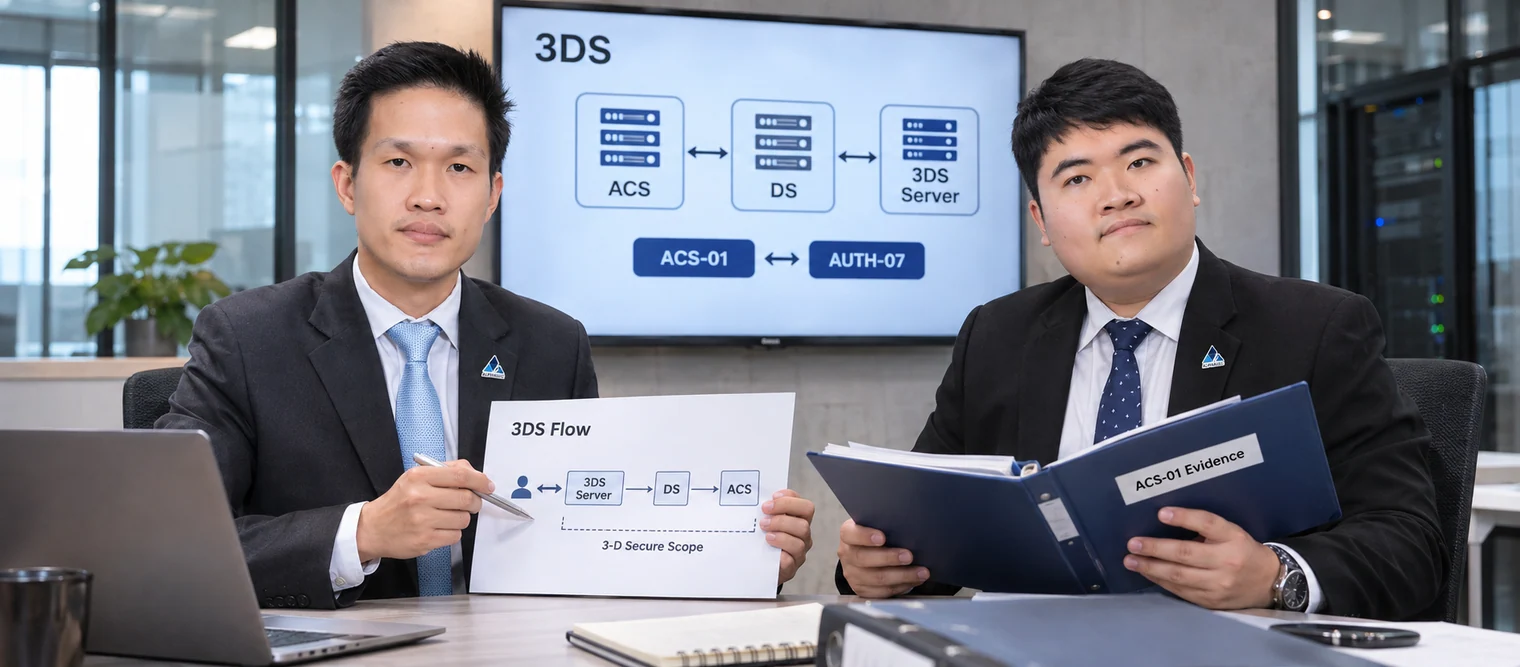
Illustrative scene with the ALPHASEC team · Payment specialists tracing an online authentication flow
Illustrative evidenceAssessment boundary
3DS · ACS / DS / 3DS Server
Illustrative evidenceControl under review
ACS-01 ↔ AUTH-07 · evidence
Illustrative evidenceExample result
ACS-01 → finding → system owner
The provider identifies its role in the online authentication flow.
Discuss this service

PCI P2PE QSA

Point-to-Point Encryption assessment of applicable payment solutions, components and applications. Review protection from payment-data capture to secure decryption, with attention to cryptographic key management, device handling and operating procedures.

How is payment data protected from capture to decryption?
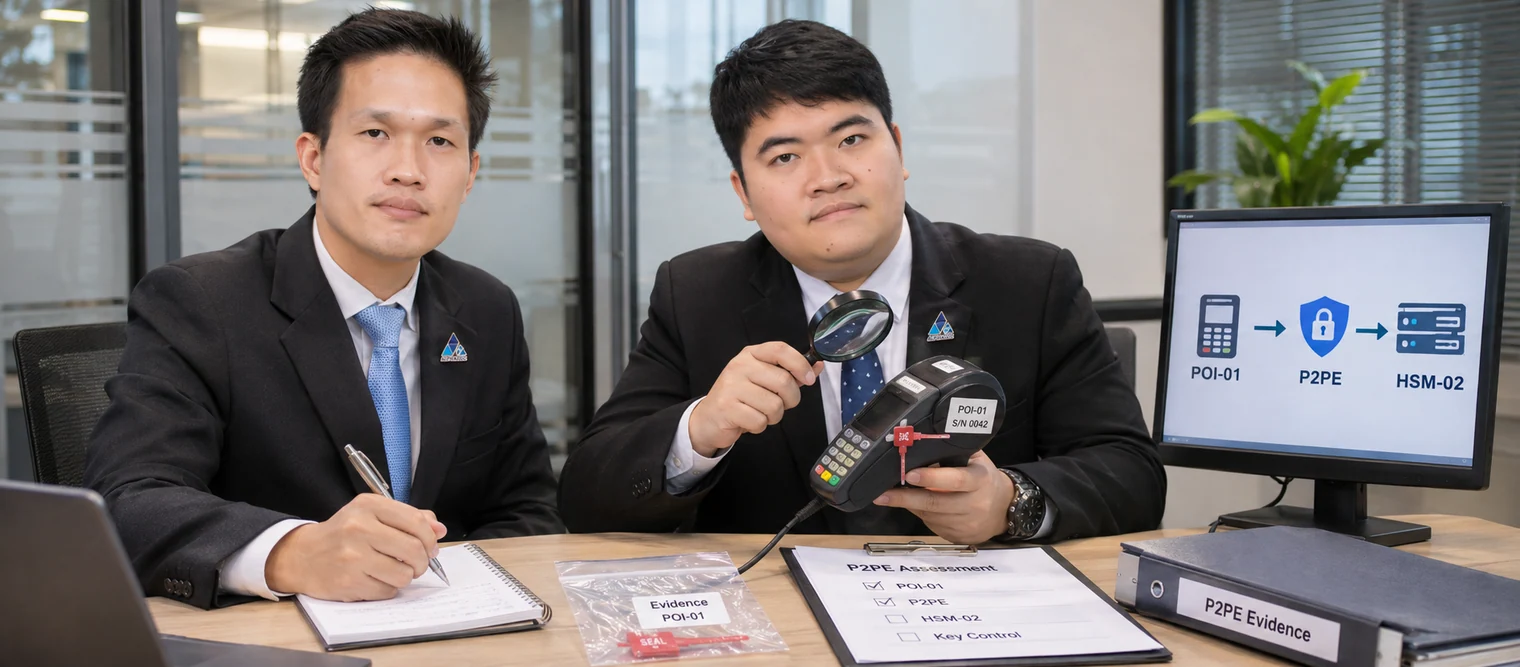
Illustrative scene with the ALPHASEC team · A technician inspecting a payment terminal and its tamper-evident seal
Illustrative evidenceData flow
POI-01 → P2PE → HSM-02
Illustrative evidenceSupporting evidence
POI-01 · S/N 0042 ↔ key custody
Illustrative evidenceFollow-up action
POI-01 / HSM-02 · in review
The provider identifies capture devices, components and the decryption environment.
Discuss this service

Frequently asked questions

Is ALPHASEC a PCI QSA company?

ALPHASEC supports PCI DSS scoping, readiness and QSA assessment for merchants and service providers, with ROC/AOC reporting or SAQ support as applicable.

Do we need a ROC or an SAQ?

It depends on your merchant or service provider level, payment channels and the requirements of your acquirer or card brands. We confirm the assessment path during scoping.

How do you reduce PCI DSS scope?

We map cardholder data flows, payment channels and third parties to define the cardholder data environment and identify where scope can be narrowed.

LET’S UNDERSTAND YOUR NEEDS

Tell us what
you need.

Answer the service-specific questions, review your summary, and send your request to our team.

A high-level summary is enough. Please do not include passwords, payment card data or confidential system evidence.

Read our privacy notice

For urgent matters, call 091 003 4852

Discuss your requirements directly with our team.

Contact our team

Related services

Governance, Risk & Compliance

ISO/IEC 27001 & ISMS Consulting

Build an information security management system that connects organisational context, risk and continual improvement.

↗