Privacy, Data & AI Governance
PDPA Readiness Consulting
Assess personal data practices and create a practical PDPA readiness roadmap for your organisation.

Review privacy controls and operating evidence to identify gaps and prioritise improvements.
Discuss your requirements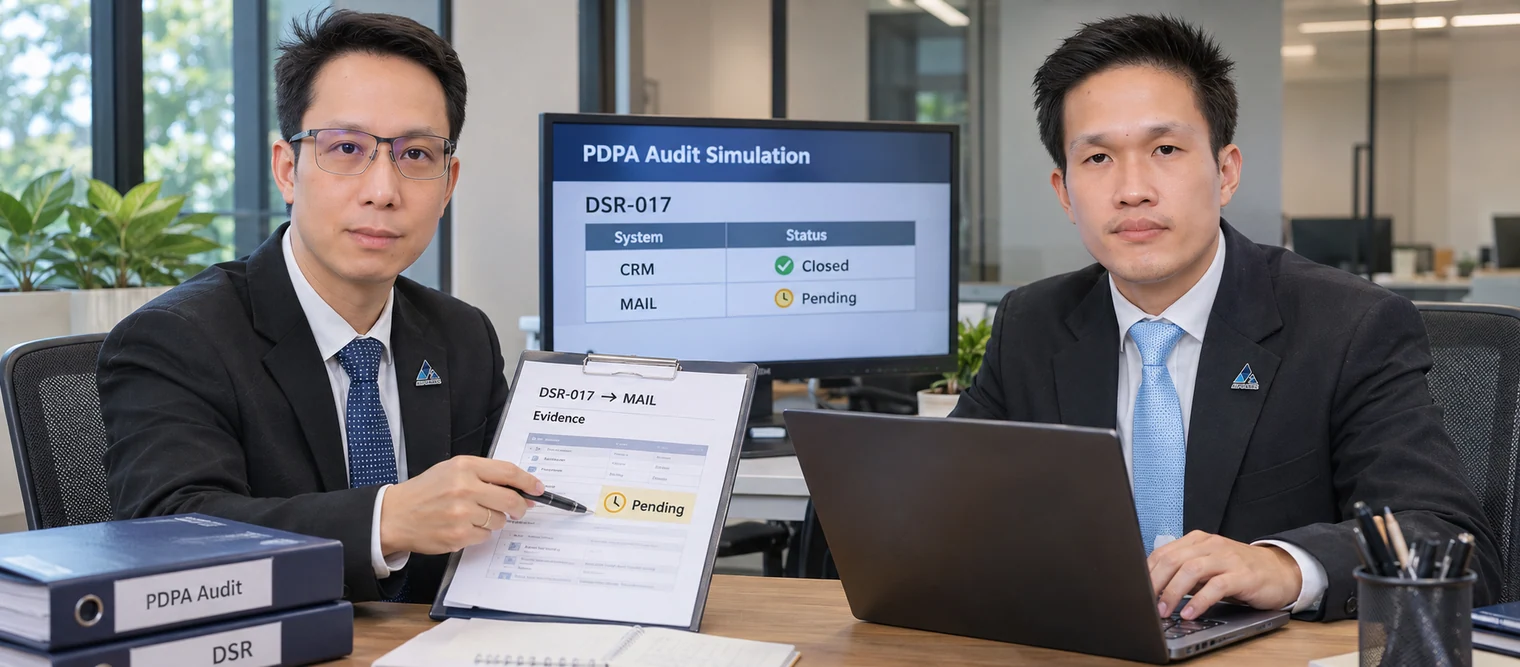
SERVICE IN DETAIL
Boards, management, internal audit and regulated organisations that need an evidence-based view of controls.
Privacy audit boundaries, processing inventory and evidence requirements
Confirm the business activities, systems, locations and assessment criteria. Establish the audit period, evidence request list and sampling approach, taking account of the independence required for the engagement.
Notices, consent records, rights requests, retention and processor oversight
Interview control owners and trace selected transactions or activities to supporting records. Evaluate both control design and operation, validate exceptions with the responsible teams and document the basis for findings.
Privacy control findings, management actions and correction evidence
Present findings with risk, evidence and practical recommendations. Agree management responses, owners and target dates; review corrective evidence where follow-up is included. Any formal assurance conclusion depends on the applicable criteria and assessment results.
We confirm the scope, responsibilities, evidence, timetable and deliverables in the proposal. The activities above are tailored to the systems and objectives agreed with your organisation.
Many organisations already have privacy notices and policies. A PDPA audit checks whether those documents match what actually happens in systems and day-to-day work, using samples and records rather than interviews alone.
The audit starts by agreeing scope, period and criteria. Auditors then request evidence, select samples, trace them through systems and processors, and discuss findings with process owners before the report is issued.
You receive findings linked to evidence, a risk rating and prioritised corrective actions. Many organisations audit annually, after significant system or process changes, or before external assessments such as ISO/IEC 27701. If gaps are found, PDPA consulting can help close them.
Privacy controls and operating evidence, such as the processing inventory, consent and notices, data subject requests and processor arrangements, within the agreed scope.
An audit tests whether existing controls operate as documented. Consulting helps design and implement those controls.
Findings showing where recorded status differs from available evidence, and prioritised corrective actions.
Answer the service-specific questions, review your summary, and send your request to our team.
A high-level summary is enough. Please do not include passwords, payment card data or confidential system evidence.
For urgent matters, call 091 003 4852
Discuss your requirements directly with our team.
Contact our teamAssess personal data practices and create a practical PDPA readiness roadmap for your organisation.
Review security measures around personal data and align improvement priorities with processing risks.
Design a privacy operating programme with clear ownership, workflows and evidence for ongoing management.