Privacy, Data & AI Governance
Data Security Measures
Technical and organisational measures for personal data.
Reduce the risk of sensitive data leaving your organisation with DLP rules designed around your data, tested on real channels and workable for your staff.
Discuss your DLP scope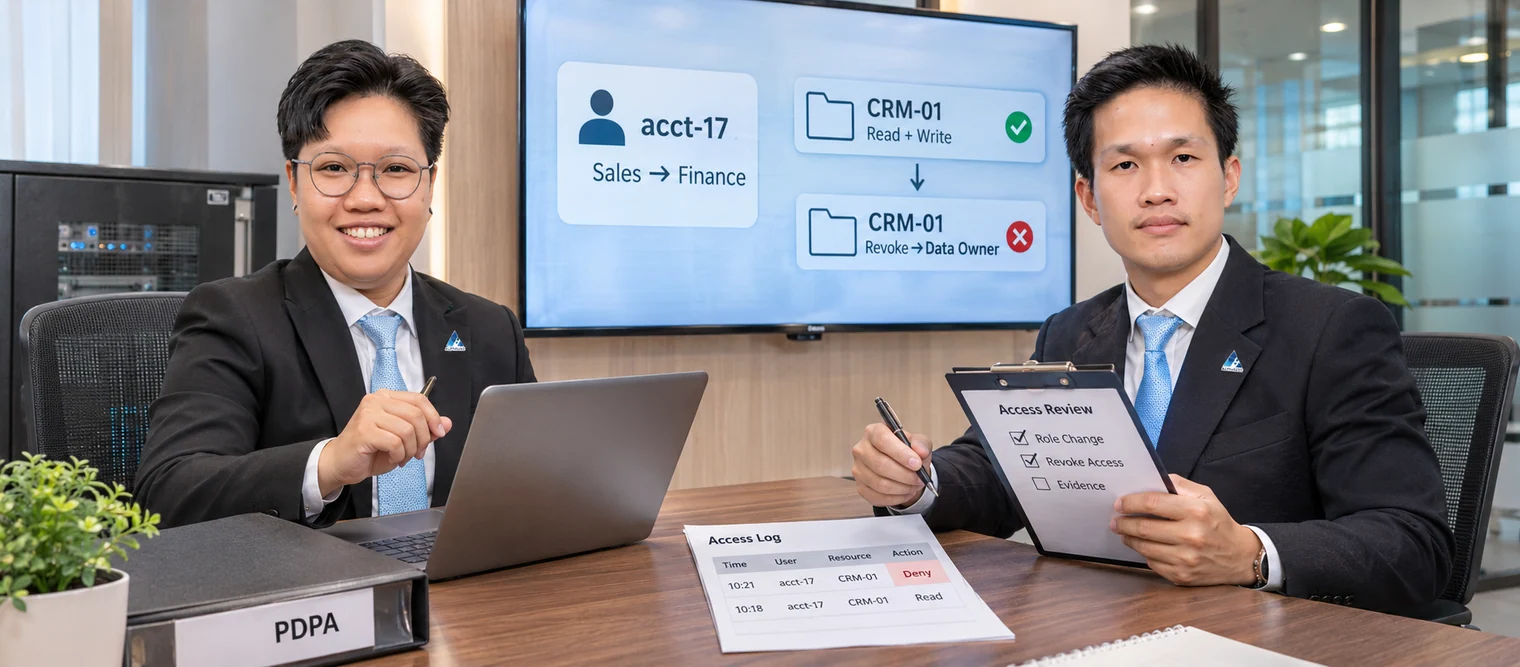
Data Loss Prevention (DLP) is the combination of tools, policies and processes that find sensitive data and control how it is used and shared. A DLP rule might warn a user before a customer list is sent to a personal email address, block a copy to USB, or alert the security team when confidential files are uploaded to an unapproved cloud service.
Thailand's Personal Data Protection Act requires data controllers to maintain appropriate security measures to prevent unauthorised loss, access, use, change or disclosure of personal data. DLP is one technical measure that supports this alongside access control, encryption and monitoring; it does not make an organisation compliant on its own. See Data Security Measures and PDPA consulting.
Data classification labels information by sensitivity. DLP uses those labels and content patterns to detect and control how the data moves. Classification usually comes first.
Not always. Many organisations already have DLP features in their email, endpoint or cloud licences. We review what you have before recommending additional tools.
Well-tuned rules mostly run in the background. Starting in monitor mode and adding clear user messages and an exception process keeps disruption low.
No. DLP supports the security measures the PDPA expects, but compliance also needs governance, records of processing, data subject rights handling and other controls.
It depends on the number of channels, users and data types. Most projects start with a pilot on one or two channels; we confirm the plan after requirements are agreed.
Answer the service-specific questions, review your summary, and send your request to our team.
A high-level summary is enough. Please do not include passwords, payment card data or confidential system evidence.
For urgent matters, call 091 003 4852
Discuss your requirements directly with our team.
Contact our teamTechnical and organisational measures for personal data.
Define data ownership, classification and lifecycle controls.
Detect and respond to threats across endpoints and servers.
Protect confidential and prototype data for automotive customers.