THREAT INTELLIGENCE
SANS ISC / DShield · 
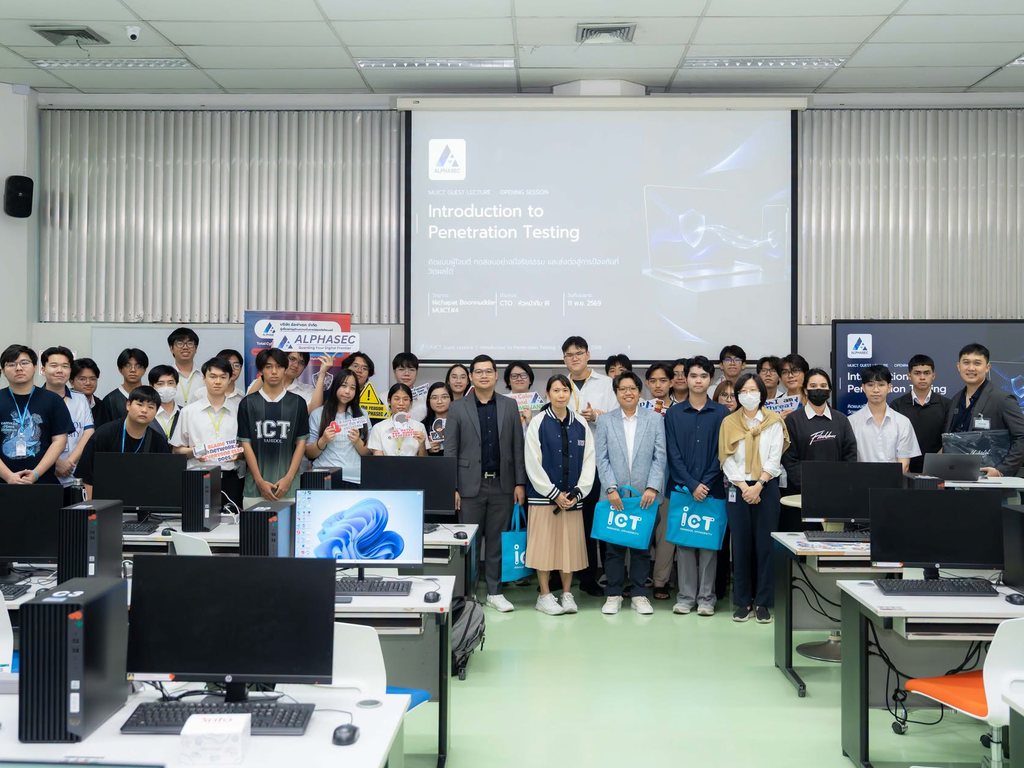
Cybersecurity Club, Faculty of ICT, Mahidol University

Build cyber resilience, protect personal data and govern AI with specialists supporting your organisation from planning through incident response.
+66 91 003 4852Four anonymized engagements spanning incident investigation, security testing and compliance assessment.
When an organization faced a cyberattack, ALPHASEC worked alongside its team—from containment and forensic investigation to legal coordination, regulator correspondence and an improvement plan.
What the client gained: coordinated technical and legal support, with facts, documents and an action plan to help leadership make informed decisions after the incident.
Facing a cyber incident? Contact ALPHASEC091 003 4852 ↗ALPHASEC combines AI with experienced penetration testers in a Human-in-the-Loop approach to broaden test coverage, accelerate discovery and validate findings—helping organizations strengthen their defenses against AI-assisted attacks.
ALPHASEC supports banks, service providers and merchants of every size on their path to PCI DSS. Our work covers Level 1, Level 2 and Level 3 assessments, SAQs and ROCs, with platforms that make compliance activities and assessment preparation easier to manage.
ALPHASEC helps clients meet TISAX, ISO/IEC 27001 and ISO/IEC 42001 requirements, from identifying gaps and implementing management systems to developing teams, organizing evidence and preparing for external assessment. The aim is to meet partner expectations, build confidence and maintain compliance over time.
Report the incident, assess the situation and confirm the engagement.
Targets in the IR service offering
Confirm the SLA, clock-start conditions, onsite coverage and team availability in the service agreement before work begins. Without a prior agreement, response timing is confirmed per incident. These are response targets, not guaranteed resolution times.
Call with the observed symptoms, affected systems and a coordinating contact.
Assess urgency, provide initial guidance and confirm authorization, scope, secure evidence transfer and the SLA.
Coordinate containment, preserve evidence, assess cause and impact, and update stakeholders as agreed.
Deliver findings, recommendations and scoped retest results, with explicit limitations.
Prepare the observed symptoms, detection time and a coordinating contact. Do not submit passwords or sensitive evidence through a general contact form.
Explore ALPHASEC projects, partnerships and speaking engagements, newest publication first.
Newest → oldest · Publication date
Selected clients
Trusted by organisations across industries.
Swipe or use the left and right arrow keys to browse the logos.




Choose the challenge you need to solve or the outcome you want to achieve, then explore the services that support your next step.
Assess weaknesses, test security and prioritise improvements to focus investment where it matters.
Explore relevant servicesReview cloud, application and data protection, with practical improvements and tools suited to your business.
Explore relevant servicesConnect threat monitoring, detection and response with your existing teams and systems.
Explore relevant servicesContain the impact, investigate evidence and plan a secure return to operations.
Explore relevant servicesPrepare processes, controls and evidence for relevant standards and requirements.
Explore relevant servicesEstablish privacy practices, data ownership and access rules, with ongoing support for day-to-day operations.
Explore relevant servicesAssess AI readiness, risk and security, then build governance and a practical adoption roadmap.
Explore relevant servicesPlan continuity, rehearse crisis decisions and build the skills of employees and executives.
Explore relevant servicesConnect IT Audit, ITGC, cybersecurity, privacy and BCP/DRP with your IPO readiness programme.
Explore relevant servicesNot sure where to begin? Talk to ALPHASEC about the right scope for your organisation.
Talk to ALPHASECIPO READINESS · SET / mai
Prepare for a SET or mai IPO with ALPHASEC: IT audit, ITGC, cybersecurity, PDPA, business continuity, data and AI governance advisory.
From your business need to evidence, an action plan and work your team can use.
Objectives, systems, owners, timeline and deliverables.
Review, interview or test as scoped, then validate findings.
Connect risk to business impact and agree what to address first.
Executive findings, practical reports and clear next steps.
The proposal sets out the scope, timeline and deliverables for your engagement.
Agreed test plan · evidenced findings and remediation priorities · executive summary and scoped retest results
Explore service scope ↗Gap report · scoped improvement plan and documentation · assessment reporting appropriate to the engagement
Explore service scope ↗Gap report · policies and operating forms · readiness summary and outstanding actions
Explore service scope ↗Incident scope and evidence register · timeline and containment recommendations · recovery priorities and lessons learned
Explore service scope ↗Explore ISMSReady, PCIReady, DefaceGuard and BCM Ready: technology for information security management, payment security, website monitoring and business continuity.
Product example · demonstration data
Organise ISMS tasks and evidence to support ISO/IEC 27001 readiness and continuous management.
Organise PCI DSS readiness work, responses and evidence in a structured platform workflow.
Explore & enquire
Support PCI DSS readiness for travel businesses with an organised preparation workflow.
Explore & enquire
Organise ISMS tasks and evidence to support ISO/IEC 27001 readiness and continuous management.
Explore & enquire
Structure continuity planning and readiness activities for your business continuity management system.
Explore & enquire
Monitor external cyber risk signals associated with your organisation’s public-facing assets.
Explore & enquire
Track potential exposure of organisational information and accounts on the dark web for further investigation.
Explore & enquire
Monitor website changes and integrity signals to help teams investigate unexpected modifications.
Explore & enquire
Follow privacy developments, news and enforcement information in one research-oriented resource.
Explore & enquire
Structure AI system security assessment work and track findings to support remediation.
Explore & enquireConnect your needs with the right expertise. The engagement scope identifies your project lead and delivery team.
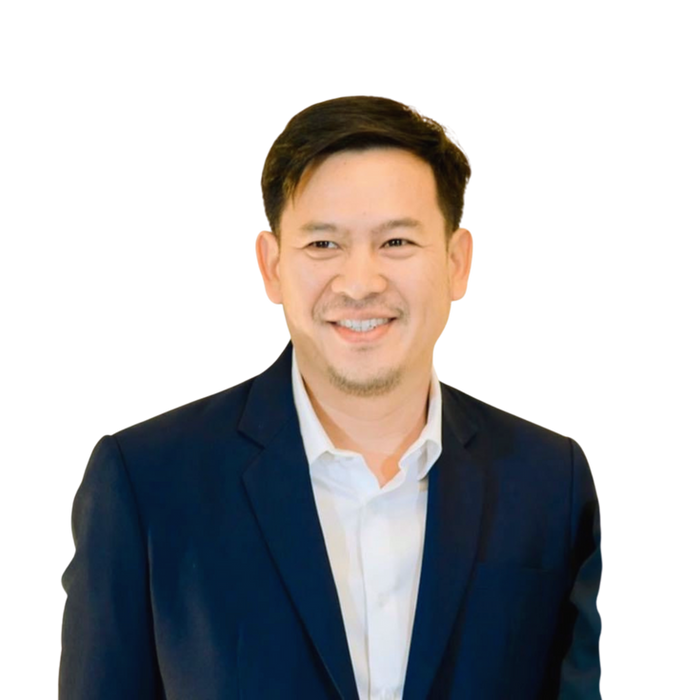
Program direction
Founder & CEO
Business goals, risk and assurance priorities
QSA · CISSP · AIGP
Profile & credentials
Cyber Defense & Technology
CTO & Principal
Security operations, incident response and technology
CompTIA CySA+
Profile & credentials
Compliance & Advisory
Principal
Standards, data governance and AI governance
CIPP/E · CIPM · CDMP
Profile & credentials
Data Protection
COO & Principal
Privacy responsibilities, processes and documentation
CIPP/E · DPO (CEPAS)
Profile & credentials
Penetration Testing
Head of Offensive Security
Penetration testing, vulnerability assessment and adversary simulation
PenTest+ · CySA+ · Security+
Explore this serviceMeet the people leading our business and specialist practices.
Connected to ALPHASEC’s existing articles and news.
วิเคราะห์ 22 เทคโนโลยี AI Cybersecurity เชื่อม Governance, Identity, Runtime และ Supply Chain พร้อมตัวอย่าง ตัวชี้วัด และแผน 90 วันสำหรับองค์กรไทย
Read articleเข้าใจ Red Teaming และความต่างจาก Penetration Testing พร้อมตัวชี้วัดการตรวจจับ การตอบสนอง การกู้คืน และแผนเริ่มต้น 90 วันสำหรับองค์กรไทย
Read articleแนวทาง AI Governance สำหรับองค์กร เชื่อม ISO/IEC 42001, Data Governance, PDPA และ AI Security พร้อมตัวอย่างควบคุม AI Agent และแผนเริ่มต้น 90 วัน
Read articleArticles from the ALPHASEC blog
Explore all articles